Kilyos Çay Bahçesi is a sea-view café-restaurant on the Kilyos shore (Sarıyer/Istanbul), serving everything from breakfast to an evening fish menu. With a QR-menu-based digital ordering system, hot/cold coffees, brewed teas, desserts and snacks, it hosts Istanbulites on weekend coastal trips and Kilyos beach visitors. The warm brown-copper brand carries a classic tea-garden identity into a friendly tone with Great Vibes + Open Sans typography.
HOSPITALITY · CYBERSECURITY & RECOVERY
Kilyos Çay Bahçesi
Malware removal, website recovery, and ongoing server services for Kilyos Çay Bahçesi — securing a stable digital presence after compromise.
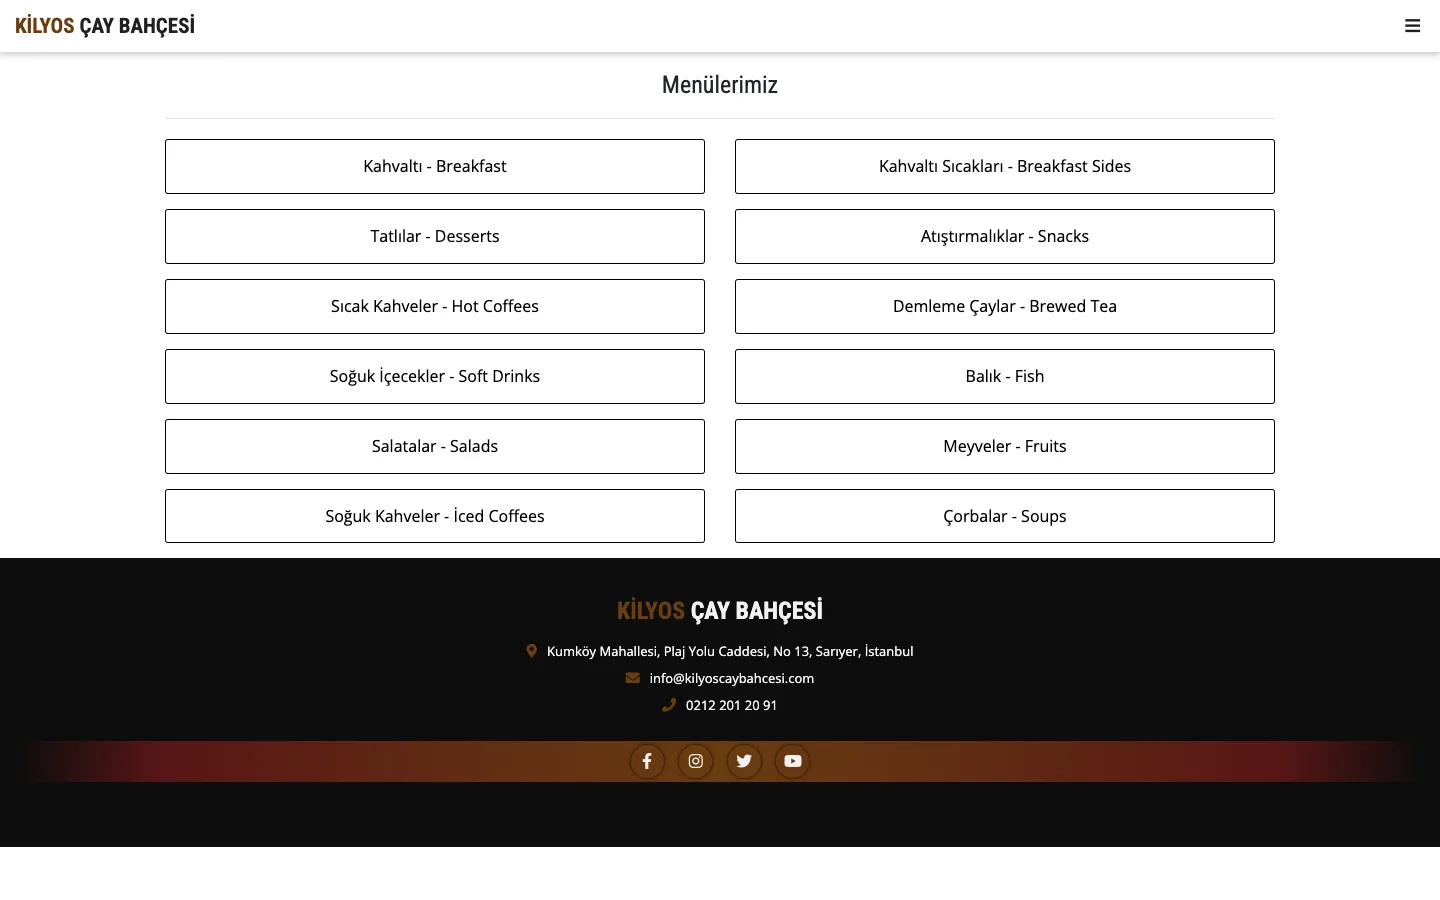
PROJECT GALLERY
Screens from the delivered digital experience
PROJECT STORY
Project overview and scope
Malware removal, website recovery, and ongoing server services for Kilyos Çay Bahçesi — securing a stable digital presence after compromise.
The site had been infected, triggering Google safe browsing warnings and uncontrolled content changes. Urgent cleanup, hardening, backups and long-term protection were required.
The site had been infected, triggering Google safe-browsing warnings, and content was being altered without authorisation. The business was in peak season; cleanup + hardening + backup had to happen within hours. QR-menu traffic must not be interrupted, no hidden backdoors should remain, and Google ranking had to recover the moment the warning was lifted.
A forensic server review was completed: modified PHP files were compared with trusted sources, and identified malware injections and suspicious cron entries were removed. Imunify360, key-only SSH, fail2ban and WAF controls were configured. A review was initiated through Google Search Console and its outcome tracked in the maintenance record.
DELIVERABLES
Modules completed within the project
- 01Emergency malware and backdoor cleanup
- 02Server hardening and file-integrity verification
- 03Backup strategy and disaster recovery planning
- 04Ongoing server services and monitoring
- 05Management of SSL and hosting renewal processes
TECHNOLOGY STACK
Platforms and tools used
Imunify360WAFfail2banSSH key-onlyJetBackupLiteSpeedCloudflare
Cleaned
Malicious files
WAF
Hardening layer
Scheduled
Backups
Alarm
Active monitoring
AIOR PROJECT NOTE
During a mid-season security incident, the priorities are to contain damage, validate a clean recovery point and restore critical journeys such as the QR menu in a controlled way.
Delivered scope and continuity
Malicious files were removed, Google's safe-browsing review process was completed, and file-integrity and backup checks were added to the maintenance plan. No security layer eliminates future infection risk.